← Work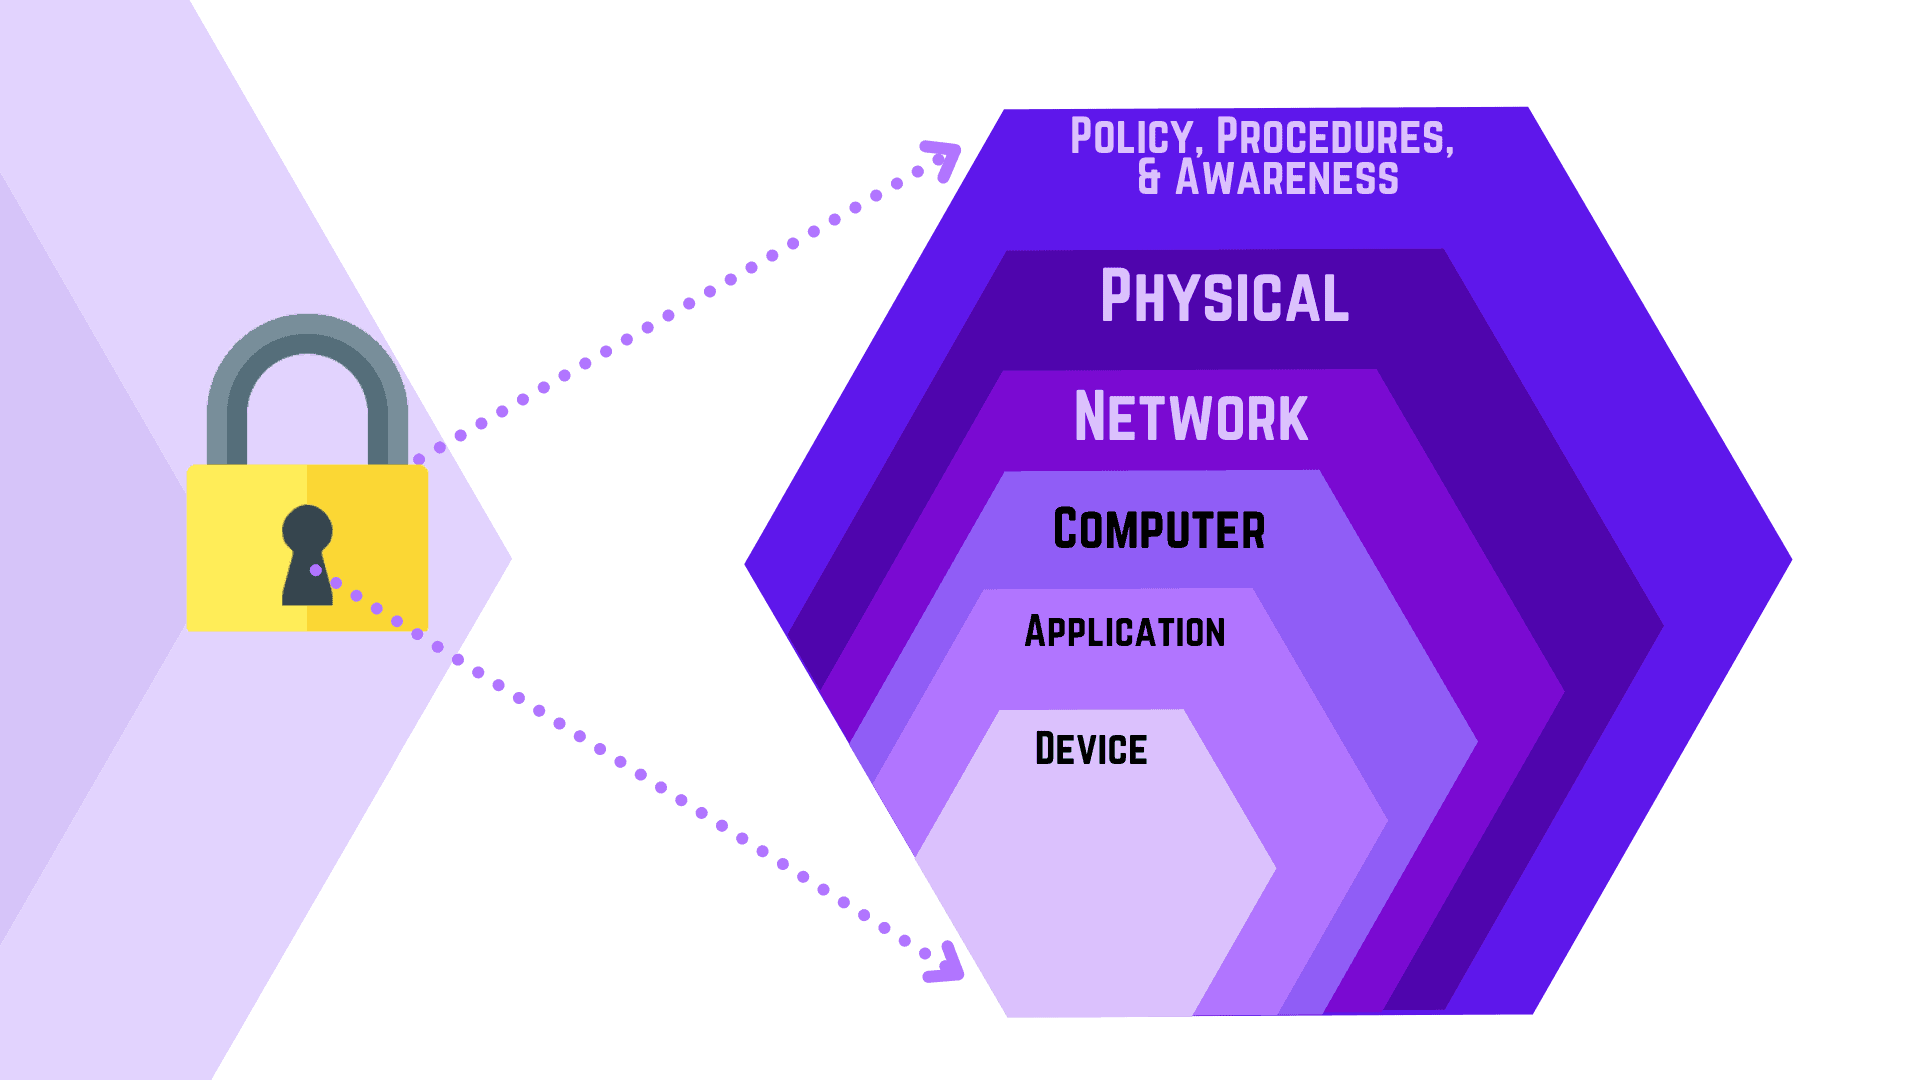
PRJ · 2019
Cyber Security and Vulnerability Implementation
Built an access-certification governance process and a continuous vulnerability management program for a healthcare client.
The situation
A healthcare client needed to protect patient and business data from internal and external threats, and to know who had access to which applications.
What I did
- Access certification. Delivered the governance process framework for certifying application access — regular, recorded reviews of who can reach which systems — and introduced standards for the transformation work that followed.
- Security baseline. Evaluated the environment against security best practices and implemented the missing controls.
- Vulnerability management. Set up a continuous four-step cycle — scan, assess risk, prioritize and fix, repeat — to find weaknesses in procedures, design, implementation or internal controls before they could be triggered by accident or exploited on purpose.